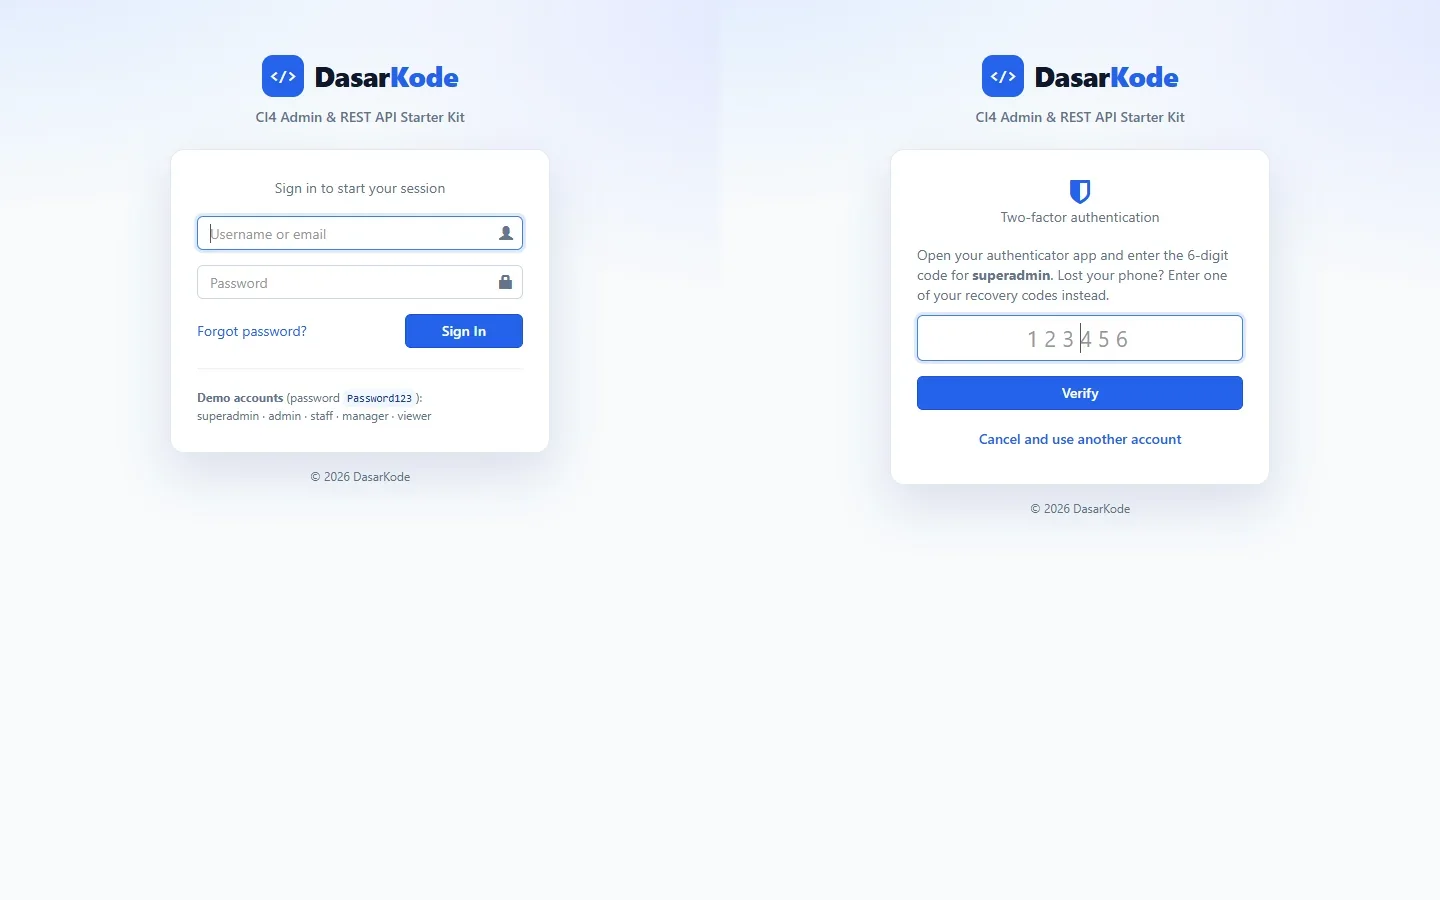
A secure login
- Log in with username or email
- Forgot & reset password by email (single-use token)
- Per-IP rate limiting + automatic account lockout
- Forced password change on first login
- CSRF, security headers, HttpOnly cookies, bcrypt
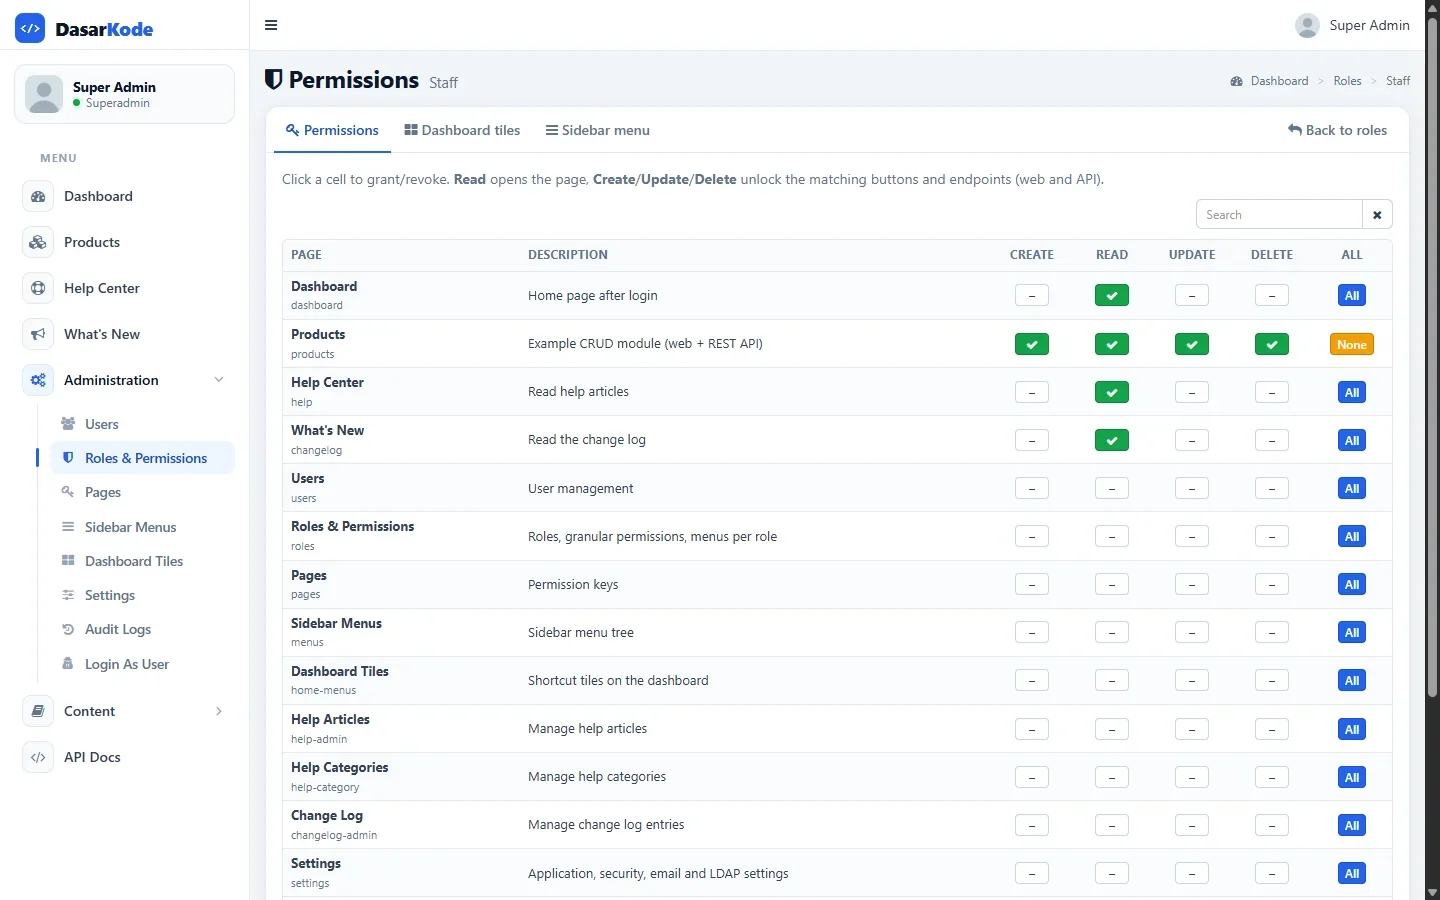
A login system built on if ($role == 'admin') falls apart fast. The CI4 Starter Kit uses granular roles & permissions: every page gets Create/Read/Update/Delete flags per role, menus adapt automatically, and it's all managed from the UI.
One-time payment · unlimited projects · In Indonesia? Lynk.id QRIS/VA
Click a screenshot to enlarge it. The full demo video is on the main page.
Most CodeIgniter 4 login examples store a single role column on the users table and check it with if-else in controllers and views. The moment you need something new, say a Finance role that can view records but not delete them, you're combing through dozens of files.
This kit replaces that with RBAC: a user has one or more roles, each role has permissions per page, and routes are guarded by filters. Adding a role happens in the admin UI, without touching code.
Example: a Finance role that can only view and create invoices.
Under Roles & Permissions, create Finance and tick Read and Create for the invoices page. Leave Update and Delete off.
Routes the role isn't allowed to use are rejected, even if someone types the URL directly.
$routes->get('invoices', 'Admin\Invoices::index', $p('invoices'));
$routes->post('invoices/(:num)/delete', 'Admin\Invoices::delete/$1', $p('invoices', 'delete'));For example, to hide a button or a column.
$canEdit = $this->can('update');           // current page
$canSeeUsers = $this->can('read', 'users'); // another pageIn User Management, pick one or more roles. Sidebar menus, dashboard tiles, and action buttons update immediately.
| Feature | "role" column | CI4 Starter Kit |
|---|---|---|
| Different menus per role | if-else in views | Automatic from permissions |
| Adding a new role | Edit many files | From the admin UI |
| Per-action permissions: view, create, edit, delete | ✕ No | ✓ Yes |
| One user with several roles | ✕ No | ✓ Yes |
| Password reset by email | Sometimes | ✓ Yes |
| 2FA, rate limit & lockout | ✕ No | ✓ Yes |
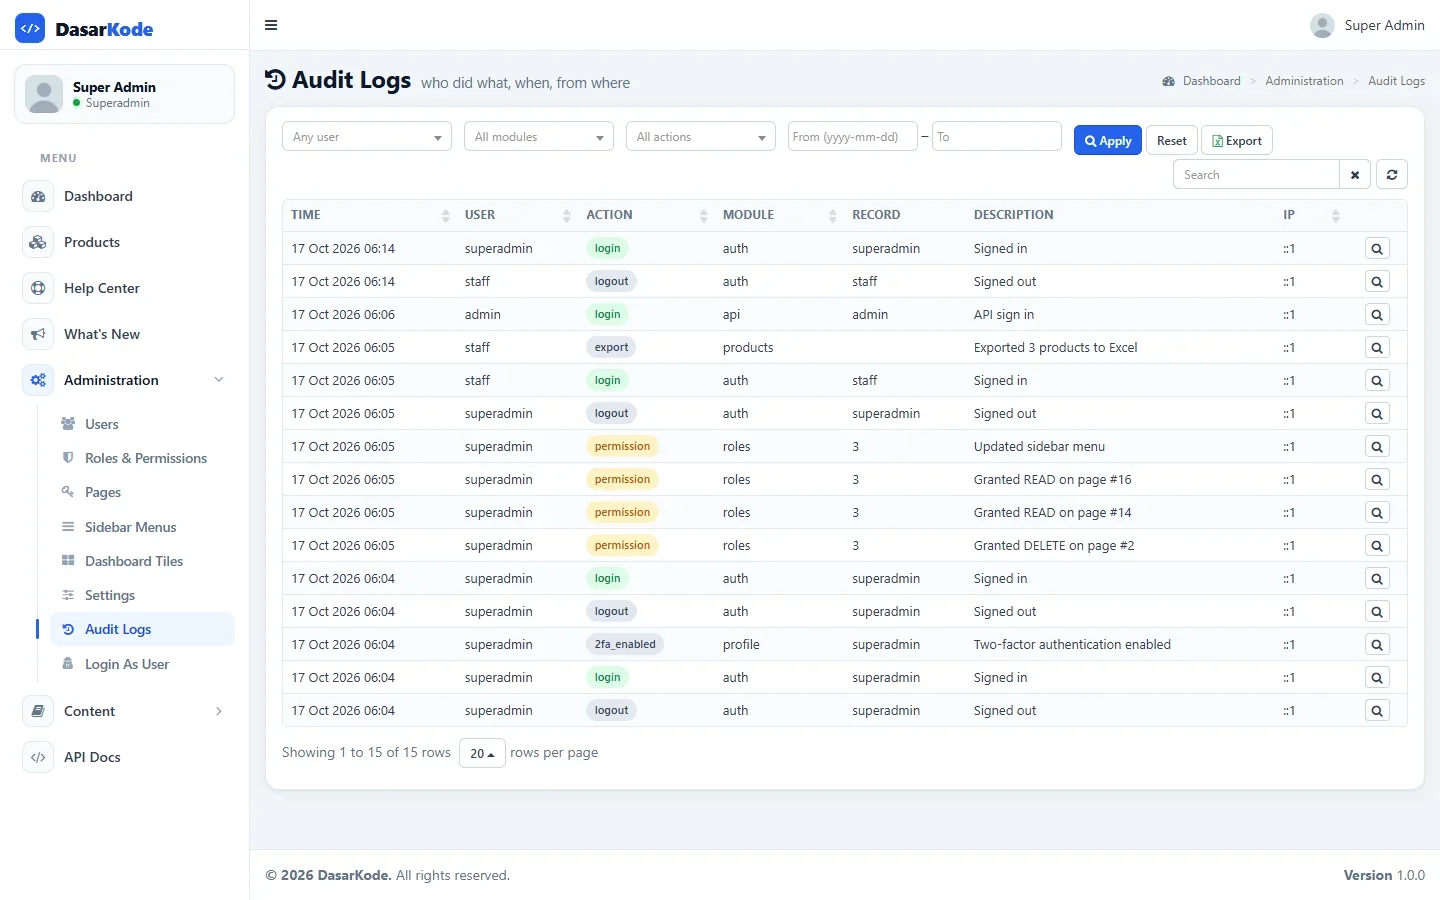
| Audit log | ✕ No | ✓ Yes |
Shield is CodeIgniter's official authentication library: it gives you login plus groups and permissions in code, but no admin screens. The CI4 Starter Kit is a complete application with its own auth (no Shield dependency) and the UI to manage users, roles, permissions, menus, and the audit log.
As many as you need. The demo seeder includes 6 accounts with different roles as examples, and new roles can be added any time from the admin UI.
No. 2FA is optional, works with authenticator apps like Google Authenticator, and comes with recovery codes in case a phone is lost.
Yes, optionally. The LDAP/AD server is configured from the Settings menu without code changes, and the bind password is stored encrypted. If you don't use it, login works with regular local accounts.
Login, RBAC, dynamic menus, audit log, JWT REST API, Docker, and docs in English and Indonesian. Pay once, with help until it runs.